St. Luke’s Mobile App Data Incident: What Developers Can Learn
What St. Luke’s disclosed about its mobile app data incident, what remains unknown, and practical lessons for developers building connected applications.
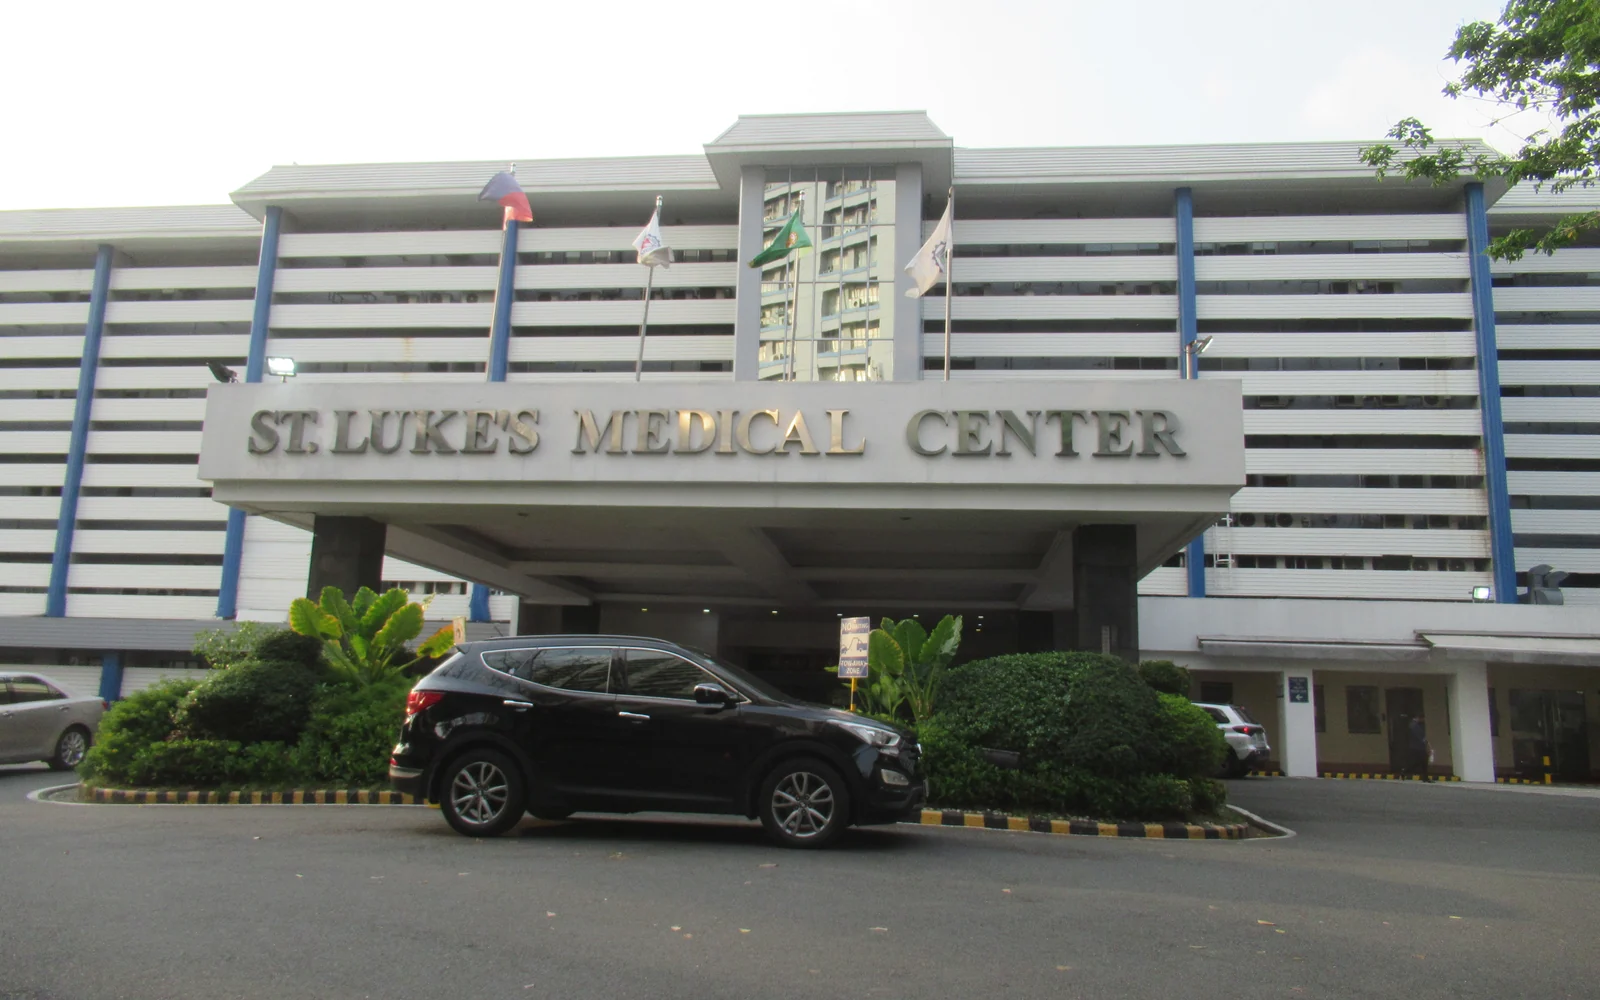
A mobile app can be one part of a much larger system. Behind its screens are services, identities, databases, integrations, and the teams responsible for them. The reported St. Luke’s Medical Center data incident in the Philippines is a useful starting point for understanding these boundaries, provided we keep public statements separate from assumptions about what happened.
What the hospital and regulator have said
St. Luke’s published an official notice dated October 30, 2026. It described unauthorized access to a third-party-managed platform supporting its mobile application, with possible effects on some patients’ and employees’ personal information. The hospital said it introduced containment measures, engaged independent cybersecurity specialists, and would contact people whose information might be involved.
GMA News reported a further hospital statement on November 3, describing an incident detected on October 29. According to that statement, the affected platform was isolated, the app was taken offline, and the hospital’s electronic medical records (EMR) and other core clinical systems were unaffected.
Back End News reported on November 3 that NPC spokesperson and Deputy Privacy Commissioner Jose Belarmino II confirmed receipt of the hospital’s notification on October 30. The National Privacy Commission was reviewing it under its established process. A notification review is not a published conclusion about responsibility or the cause.
What remains unknown
The public sources reviewed for this article do not establish the initial access method, identify an attacker, or provide a final forensic explanation. They also do not give a confirmed total of affected individuals or a definitive list of exposed data fields.
Personal information associated with patients is not automatically the same thing as a complete medical chart. Similarly, an app incident does not by itself establish a ransomware event or a compromise of every connected hospital system. Accurate reporting needs evidence for each of those separate claims.
The app is only one part of the system
In a typical connected application, the phone displays information while a backend API decides which requests to accept. That service may call a provider, send a notification, or retrieve a permitted subset of data. A single successful screen interaction can therefore cross several security boundaries.
For your own project, draw the actual data flow before reviewing individual screens. Identify the service handling each request, the identity it uses, and the information crossing into the next system. OWASP’s mobile testing guidance treats architecture and backend services as part of understanding the application’s security.
| Component | Question for the development team |
|---|---|
| Mobile or web client | What information does the device store, and which backend services does it call? |
| Application API | Which server-side checks permit each read or update? |
| External provider | What data and credentials does this integration need? |
| Core system | Which connections are explicitly permitted, and who approves them? |
Authentication and authorization solve different problems
Authentication establishes an identity, such as a signed-in user. Authorization decides whether that identity may perform a particular action on a particular resource. Passing a login check does not answer every permission question.
Consider a fictional appointment application in a test environment. Two test accounts should each see their own appointments. A useful regression test checks that one account cannot read or change the other account’s appointment, even when it sends a valid request directly to the backend. The test must also cover legitimate delegated access where the product supports it.
OWASP calls missing resource-specific checks broken object-level authorization. Its guidance is to verify the user’s permission for the requested operation and resource at the API. Hiding a button or choosing hard-to-guess identifiers does not replace that decision.
Treat third-party integrations as explicit boundaries
Using a provider can give a team specialist capabilities and operational support. It also creates interfaces that need clear ownership. For your own integration, document the permitted data, service identity, environments, support contacts, and the person able to disable the connection.
OWASP’s guidance on unsafe API consumption recommends assessing providers’ API security, using encrypted transport, validating returned data, and controlling redirects. A familiar provider name is not a substitute for these checks.
Write down the integration contract in terms that can be tested: accepted response fields, error behavior, timeouts, and what happens when a provider is unavailable. These are questions for any connected application; the hospital’s disclosure does not establish that an API-consumption weakness caused its incident.
Limit how far one component can reach
Separate systems can have different permissions and exposure. For example, a public appointment service may need a narrow scheduling interface without needing unrestricted access to every internal database. OWASP’s network segmentation guidance discusses separating application layers and controlling communication between services.
For a team reviewing its own deployment, check both the diagram and the configuration. Which network paths exist? Which service accounts can use them? Can a credential intended for a limited task reach unrelated data? A boundary is useful when deployed controls enforce it and tests verify its behavior.
The hospital’s statement about unaffected clinical systems should be reported as its assessment. It does not reveal the exact architecture or prove which particular control limited the incident.
Make logs useful without copying sensitive information
An incident investigation needs a reliable record of activity. Application events can help connect a request to its time, service, action, and outcome. Logs should support investigation without becoming a second uncontrolled store of the information the application is meant to protect.
OWASP’s Logging Cheat Sheet advises excluding or appropriately protecting secrets, access tokens, and sensitive personal information. Record the context needed for a security decision rather than dumping entire request bodies or medical content into an error tracker.
Teams should also restrict access to logs, protect their integrity, and define retention. Check sample production-shaped events with synthetic data before release. A useful team exercise is to trace one failed authorization decision across services without exposing a token or a person’s private information.
Containment and recovery need an agreed plan
Taking an application offline can be a containment decision while responders determine scope. It is not, by itself, evidence that the underlying cause has been removed or that the service is ready to return.
NIST SP 800-61 Revision 3 integrates preparation, detection, response, and recovery into risk management. For a development team, a practical application is to agree in advance who can isolate a service, preserve evidence, coordinate with a provider, and approve restoration. Reopening should follow documented checks, with monitoring for renewed suspicious activity.
In a healthcare setting, service changes also need coordination with the people responsible for patient care and continuity. This is a general planning consideration, not a claim about the hospital’s response quality.
A practical review for your own team
Turn the security discussion into a small set of reviewable records. Start with a feature your team already owns and track the evidence alongside the work.
| Review area | Concrete evidence |
|---|---|
| System ownership | Current service inventory and named escalation contacts. |
| Access control | Tests for allowed and denied actions across representative roles. |
| Provider connection | Documented data contract and expected failure behavior. |
| Service boundaries | Reviewed network rules and service-account permissions. |
| Observability | Redacted sample events and a verified alert route. |
| Response readiness | A practiced isolation and restoration checklist. |
How to read the next update
Look for specific changes to the evidence: a confirmed scope, affected data categories, investigation findings, or an official restoration notice. Keep the date and speaker attached to each statement. A later finding may narrow or expand an earlier assessment.
For developers, the durable lesson is to understand the whole request path and make responsibilities testable. That work is useful across mobile apps, websites, and internal tools, even when a public incident’s technical cause remains undisclosed.
Common questions
Frequently Asked Questions
What happened to the St. Luke’s mobile app?
The hospital disclosed unauthorized access to a third-party-managed platform supporting its app. Its follow-up statement, reported by GMA News, said the platform was isolated and the app taken offline.
Does this confirm that complete medical records were stolen?
No such conclusion is established by the sources reviewed. St. Luke’s said its EMR and core clinical systems were unaffected. The full scope of affected personal information remains unconfirmed in those public sources.
Is the cause of the incident publicly established?
The sources reviewed as of November 4, 2026 do not provide a final forensic explanation. The security controls discussed here are general learning material, not a diagnosis of this incident.
Verified references
Sources & Methodology
Incident reporting was checked on November 4, 2026. The hospital’s October 30 notice is a primary source; GMA News and Back End News report subsequent statements. OWASP and NIST support the general technical guidance. No independent investigation of the hospital’s systems was performed. The real file photograph is separately licensed as indicated in its caption.
- Notice on a Data Security Incident, October 30, 2026St. Luke’s Medical Center: Primary hospital notice; its statement is embedded as an image.
- St. Luke’s Medical Center probing cybersecurity incident on mobile appGMA News, November 3, 2026: Reports the hospital’s follow-up statement, including containment and its assessment of clinical systems.
- NPC reviews St. Luke’s reported data breachBack End News, November 3, 2026: Reports the NPC spokesperson’s confirmation of receipt and ongoing notification review.
- Logging Cheat SheetOWASP
- Quezon City Buildings Roads 37.jpgGdfrdymldo1999 / Wikimedia Commons: Original photograph dated April 5, 2023; cropped, resized, and converted to WebP.
- Photo license: Creative Commons Attribution-ShareAlike 4.0Creative Commons: Applies to the hospital photograph and its adaptation, not to the article text.
A practical next step
Review one application boundary
Choose one service your team owns. Document who can call it, what data it can return, and the test that verifies those permissions.
About the author
Wayne Pastoral
Full-stack developer behind Conduit Code Labs, working across Shopify, WordPress, web applications, performance, accessibility, and integrations.
Learn more about WayneContinue reading
More from Work & Technology
Canva’s Restructure: What Developers Can Learn
What Canva’s 2026 restructure means, why fragmented ownership slows software teams, and practical lessons for developers and team leads.
Read article
Europe’s Supermarket Fridge Hacks: When Cyberattacks Spoil Food
An educational look at Europe’s 2026 supermarket fridge cyberattacks, how connected refrigeration controls work, and the security lessons for businesses.
Read article
The Importance of Tone of Voice in Communication
How tone of voice shapes meaning, first impressions, and conversations, with research, TED talks, and practical examples for work and everyday life.
Read article
The Pomodoro Technique: How to Focus Better, Study Smarter, and Get More Done
A practical, research-backed guide to the Pomodoro Technique: how the 25/5 method works, what studies say about breaks and focus, and how to adapt it for studying, coding, writing, and deep work.
Read article
Why the Right Tools Matter at Work: AI, Automation, and the Small Utilities That Save Time
The right tools reduce repetitive work, shorten feedback loops, and create more room for judgment. Here is how AI, automation, and focused utilities can improve everyday work without turning the workflow into another problem.
Read article
Working From Home: What You Gain, What You Trade, and What Actually Works
Working from home can save time, improve flexibility, and create better conditions for focused work, but it can also blur boundaries and increase isolation. Here is what the research says and what makes remote work sustainable.
Read article